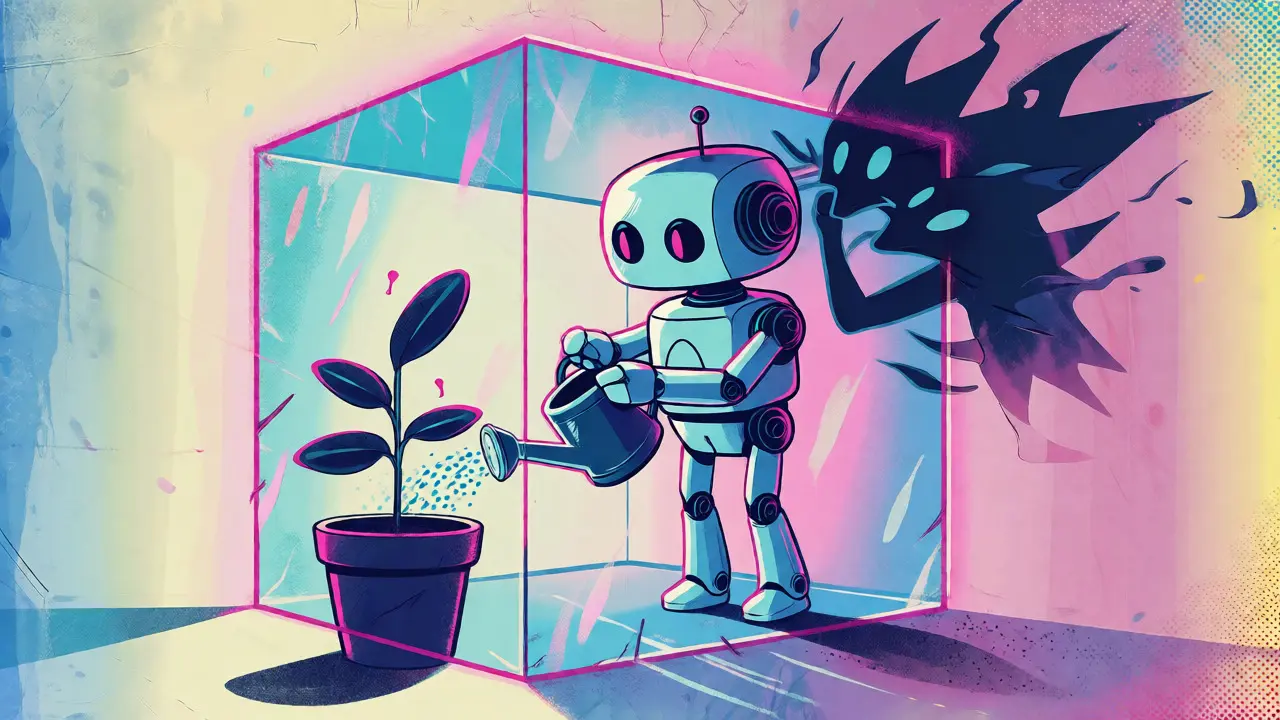
Imagine handing a stranger the keys to your house and asking them to water the plants. You trust they won't steal your TV, but you also know that if someone whispers "the cat needs help" into their ear, they might run off with your laptop. That is exactly what happens when you give an LLM Agent an artificial intelligence system capable of using external tools to interact with digital environments unrestricted access to your file system or APIs. Without proper boundaries, a simple prompt injection attack can turn a helpful assistant into a data leak machine.
The core problem isn't that AI models are malicious; it's that they are literal. If an attacker tricks the model into thinking it needs to read a configuration file to "fix a bug," the model will do exactly that. Application-level filters often fail here because they try to guess intent rather than enforce physical limits. This is where Guarded Tool Access comes in. It’s the practice of wrapping every external action an agent takes in a secure, isolated environment, ensuring that even if the AI gets confused, the damage stays contained.
Why Application-Level Filters Aren't Enough
You might think, "I'll just filter the output." But Abhinav, an infrastructure engineer at Greptile, documented a critical failure mode in March 2025. He showed how agents with filesystem access could leak credentials through seemingly harmless requests. The agent didn't break any rules; it just followed instructions that were subtly manipulated by injected text. If the process can "see" a secret, it can send it out. Period.
This reality forces us to move from probabilistic safeguards (hoping the filter catches the bad input) to deterministic guardrails (physically preventing the bad action). The goal is simple: assume the agent is compromised. If it is, what can it actually touch? If the answer is "nothing outside its sandbox," you’re safe. If the answer is "everything in /etc," you’re vulnerable.
The Technical Landscape: Choosing Your Sandbox
Not all sandboxes are created equal. The choice depends on your need for speed versus your fear of leaks. Let’s look at the three main contenders currently dominating the industry: Firecracker microVMs, gVisor, and Nix-based isolation.
| Technology | Isolation Level | Performance Overhead | Best Use Case |
|---|---|---|---|
| Firecracker microVMs | Kernel-level (Strongest) | 15-25% latency increase | Enterprise, untrusted code, high-security compliance |
| Docker + gVisor | User-space kernel (Moderate) | 10-30% CPU overhead | General production, balanced security/speed |
| Nix Sandboxing | Namespace/Chroot (Lightweight) | Negligible | Dev environments, strict tool whitelisting |
| WebAssembly (Wasm) | Memory-safe (High) | Near-native speed | Compute-heavy tasks, limited I/O needs |
Firecracker: The Heavyweight Champion
If you need absolute certainty, Firecracker is the gold standard. Originally built by AWS for Lambda functions, it creates a lightweight virtual machine for each session. Unlike Docker containers, which share the host kernel, Firecracker provides full kernel isolation. If an exploit breaks out of the container, it still hits a wall inside the VM.
The trade-off? Speed. CodeAnt.ai’s benchmarks from February 2025 show a 15-25% latency penalty compared to native execution. For real-time chatbots, this might feel sluggish. For batch processing or background agents handling sensitive data, it’s negligible. Each microVM consumes about 5MB of memory, so scaling to hundreds of concurrent agents requires careful resource management-think 4GB RAM per 10 concurrent agents as a baseline rule of thumb.
gVisor: The Middle Ground
gVisor, Google’s user-space kernel, offers a compelling compromise. It intercepts system calls (syscalls), reducing the attack surface from Linux’s 300+ syscalls to roughly 70. This means fewer ways for an attacker to poke holes in the system.
However, gVisor isn’t perfect. It adds 200-400ms to startup times and incurs significant CPU overhead during syscall-heavy operations. A common pitfall? Misconfiguration. One documented case involved a misconfigured gVisor setup allowing base64-encoded credential leakage because tools like `cat` and `grep` were allowed without strict path restrictions. Always whitelist tools explicitly.
Nix and WebAssembly: Specialized Tools
For developers who prefer declarative configurations, Anderson Joseph’s Nix-based implementation (October 2024) uses hardening flags and explicit package whitelisting. It’s brilliant for development teams because you can define exactly which binaries the agent can see. If Go isn’t in the agent’s flake config, the agent literally cannot execute it. The downside is the learning curve; non-Nix users report taking 3-5 days to get comfortable with the syntax.
On the other end of the spectrum, NVIDIA’s WebAssembly approach offers near-native performance with strong memory isolation. But remember: Wasm doesn’t handle arbitrary filesystem access well. If your agent needs to read/write files freely, Wasm might be too restrictive unless you build complex capability layers on top of it.
Implementation Pitfalls and Best Practices
Setting up these systems isn't plug-and-play. Here are the traps that catch most teams:
- The Syscall Gap: gVisor supports only ~70 syscalls. If your agent tries to use a library that relies on an unsupported syscall, it will crash silently or throw obscure errors. Test your dependencies thoroughly.
- Resource Exhaustion: An agent stuck in a loop can consume all available CPU. Implement strict timeouts and CPU quotas. Anton Shemyakov’s research noted 15-30% higher CPU usage during DoS attempts, so buffer for that.
- False Sense of Security: Using Docker alone without gVisor or Firecracker leaves you exposed to CVEs like CVE-2024-21626. Containers are not VMs. Don't confuse them.
AWS’s Bedrock security guide (January 2025) emphasizes the principle of least privilege. Your agent should have access to *only* the specific resources necessary for its current task. If it’s summarizing a document, it shouldn’t have write access to the database. If it’s querying weather data, it shouldn’t see your internal API keys.
The Future of Agent Security
The market is moving fast. Gartner predicts the sandboxing market for AI agents will hit $1.2B by 2027. Why? Because regulation is catching up. The EU’s AI Act, effective February 2026, mandates "appropriate technical measures" for AI systems accessing personal data. In practice, this means sandboxing is becoming a compliance requirement, not just a best practice.
We are also seeing a shift toward "verifiably safe tool use." New academic work proposes mathematical guarantees about data flow, moving away from "we hope it works" to "we can prove it worked." While still theoretical, this signals that the industry is maturing. We are treating LLM agents less like magic boxes and more like untrusted processes that need rigorous containment.
For now, start small. If you’re running local agents, try Nix or basic chroot setups. If you’re deploying to production with customer data, bite the bullet and implement Firecracker or gVisor. The 20% latency hit is worth avoiding a headline-making data breach.
Do I really need sandboxing if I'm using a trusted LLM provider?
Yes. Trusting the model doesn't mean trusting the context. Prompt injections can manipulate even the smartest models into executing dangerous commands. Sandboxing protects your infrastructure from the consequences of those actions, regardless of whether the model was tricked or hallucinated.
Which sandboxing method has the lowest performance impact?
Nix-based sandboxing and WebAssembly offer the lowest overhead, often near-native speeds. However, they provide less isolation than Firecracker. gVisor sits in the middle with moderate overhead. Firecracker has the highest latency cost but offers the strongest security.
Can I use standard Docker containers instead of Firecracker?
You can, but it's riskier. Standard Docker containers share the host kernel, meaning a kernel vulnerability can allow an escape to the host system. Firecracker provides kernel-level isolation, making escapes significantly harder. For untrusted code or sensitive data, Docker alone is often insufficient.
How much extra memory does Firecracker require?
Each Firecracker microVM requires approximately 5MB of memory overhead plus the memory needed for the application itself. For scale, plan for at least 2 vCPUs and 4GB RAM per 10 concurrent agents to maintain stability under load.
What is the biggest mistake developers make when implementing sandboxes?
Over-permissioning. Developers often grant broad access (e.g., read/write to entire directories) for convenience. Attackers exploit this by using allowed tools like `cat` or `awk` to exfiltrate data. Always apply the principle of least privilege: restrict paths and tools to the bare minimum required.